What should a Cybersecurity Analyst resume include?
A cybersecurity analyst resume should include a short summary, a skills section covering SIEM, incident response, vulnerability management and frameworks, experience bullets with alert volumes, response times and risk reductions, certifications such as Security+, CySA+ or CISSP, and education. Build it on FixDoks and avoid confidential detail about past employers.
Cybersecurity Analyst Resume at a glance
| Design | Bold, ATS-friendly |
|---|---|
| Sample | PDF and Word download |
| Examples | 14 bullet points, 24 skills |
| Processing | On our server over HTTPS; files are deleted right after conversion |
| Max file size | 50 MB per file |
| Price | Free to use, no watermark |
| Download | First download free, then ₹49 for 2 months of unlimited downloads (US$3 outside India) |
| Files at once | 1 free, up to 30 with a plan |
| Works on | Chrome, Edge, Safari and Firefox on Windows, Mac, Android and iPhone |
How to use Cybersecurity Analyst Resume Template
- Click Use this template to open the builder with the Bold design and a Cybersecurity Analyst section order, or Edit this example to start from the sample.
- Fill in your details. Use Examples and Skills by job for ready-made lines, or the AI writer for your own notes.
- Check the resume score, paste the job ad to see missing keywords, then download your PDF.
Cybersecurity Analyst resume sample
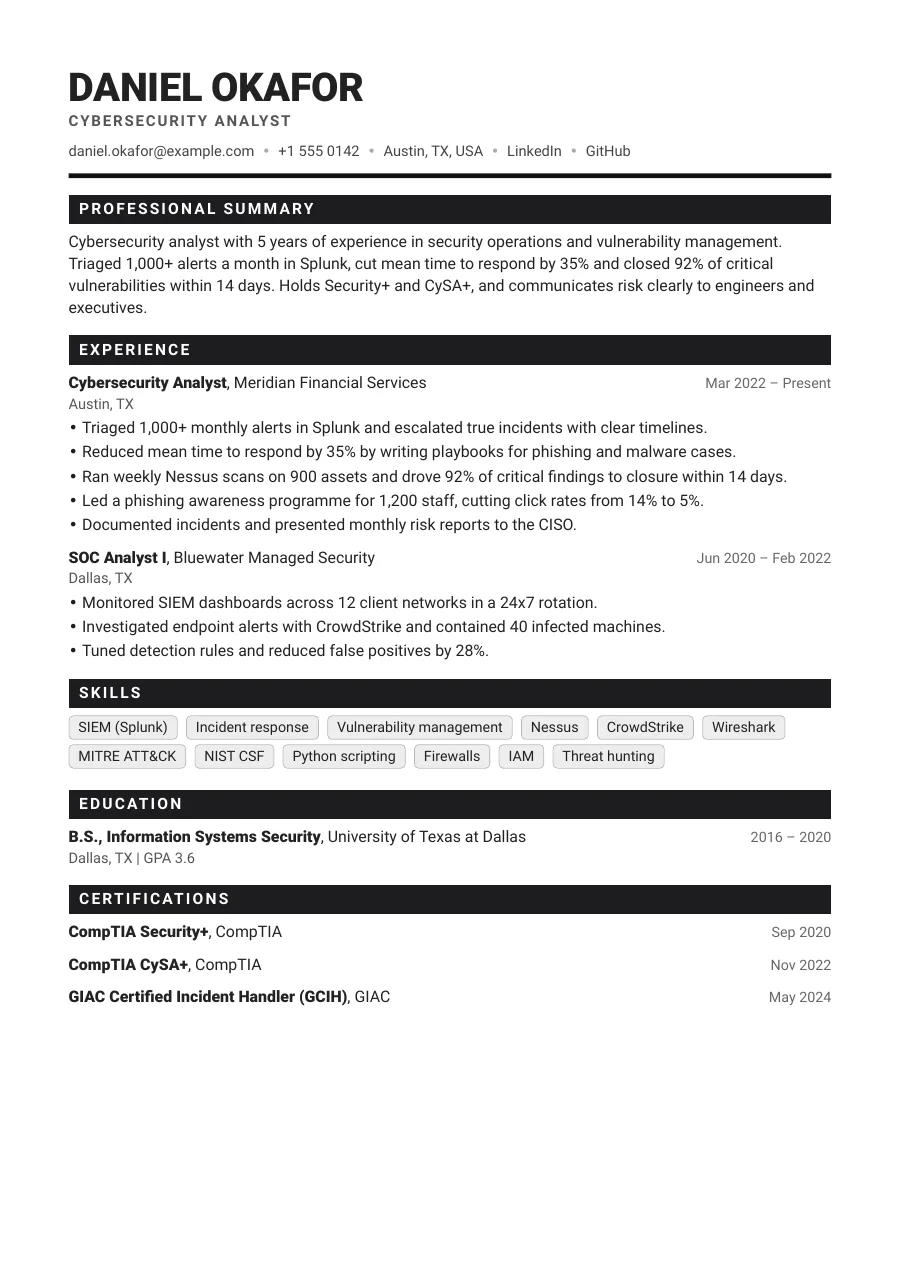
What recruiters look for in a cybersecurity analyst
Hiring managers want analysts who can detect, investigate and communicate. They check for tools and frameworks, but they care more about judgement: how you triage, what you escalate and how you document. Show the environment you protected and the outcome of your work, without giving away private details of your employer.
Best section order
- Name, contact details, LinkedIn and, if useful, GitHub or a blog
- Summary of three lines
- Skills grouped by area
- Experience
- Certifications
- Education
Certifications often act as a filter in this field, so place them high if you hold several. Entry level candidates can add a home lab or capture the flag results as a short projects section.
How to write the summary
State years of experience, the type of work (SOC, vulnerability management, cloud security), the main tools and one result. For example: five years in SOC operations, cut mean time to respond by 35%. Avoid dramatic language about hackers or protecting the world. Use the summary generator for drafts.
Bullets that show risk reduction
| Weak | Strong |
|---|---|
| Monitored security alerts | Triaged 1,000+ alerts a month in Splunk and escalated confirmed incidents with evidence |
| Performed vulnerability scans | Scanned 900 assets weekly and closed 92% of critical findings within 14 days |
| Ran phishing training | Cut phishing click rates from 14% to 5% for 1,200 employees |
Use metrics such as alert volume, time to detect or respond, closure rates, assets covered and audit outcomes. Never include client names, IP addresses or details that could expose a system.
Skills and ATS keywords
Applicant tracking systems scan for specific terms. Common ones include:
- Operations: SOC, SIEM, Splunk, QRadar, Sentinel, log analysis, incident response, threat hunting
- Vulnerability: Nessus, Qualys, patch management, penetration testing basics, CVSS
- Endpoint and network: CrowdStrike, EDR, firewalls, IDS and IPS, Wireshark
- Frameworks: NIST CSF, MITRE ATT&CK, ISO 27001, SOC 2, PCI DSS
- Scripting: Python, PowerShell, Bash
Check your wording against a posting with the ATS resume checker.
Certifications that matter
Common choices include CompTIA Security+, CySA+, CEH, GIAC certifications such as GCIH, CISSP for experienced professionals, and CISM for management tracks. Cloud security certificates from AWS, Azure or Google can help. Add the issuer and year, and only list those you currently hold.
Tailoring and formatting
Detect, protect and govern roles differ widely. A SOC posting wants alerts and playbooks, while a GRC posting wants audits and policies. Reorder your bullets accordingly, keep one column and a standard font, and save as PDF. Government and defence roles may ask about clearances; mention them only if allowed.
Entry level and home labs
If you lack professional experience, add a short projects section. Describe a lab where you set up a SIEM, collected logs, wrote detection rules or ran vulnerability scans, and say what you found. Keep names generic, state the tools, and add a link to a write-up. Capture the flag platforms can be listed with your rank, but only after real lab work.
India and abroad notes
- India: include degree, CGPA for early career, and shift availability for SOC roles. Photo is optional.
- US, UK, Canada: leave out photo and personal details. State your work authorisation and any clearance level.
Common mistakes
- A tool list with no outcomes
- Revealing confidential details about past employers
- Listing hacking claims without any context or certification
- Outdated certifications presented as current
- Skill ratings or graphics that parsers cannot read
Start from our resume templates and tailor each version to the posting.
Skills for a Cybersecurity Analyst resume
Pick the ones that are true for you and that the job ad mentions. In the builder, Skills by job adds them with one tap.
- SIEM
- Splunk
- Incident response
- Threat detection
- Threat hunting
- Vulnerability management
- Nessus
- CrowdStrike
- Wireshark
- MITRE ATT&CK
- NIST CSF
- ISO 27001
- Firewalls
- IAM
- Phishing analysis
- Log analysis
- Python
- Bash
- Risk assessment
- Security awareness
- Analytical thinking
- Communication
- Composure
- Documentation
Cybersecurity Analyst resume bullet point examples
Use these as a starting point and change the numbers and details to your own. Anything in [brackets] is a placeholder for your real figure.
- Triaged more than 1,000 alerts a month in Splunk, escalating confirmed incidents with a clear timeline and evidence.
- Reduced mean time to respond by 35% by writing incident playbooks for phishing, malware and account compromise.
- Ran weekly Nessus scans on 900 assets and brought 92% of critical vulnerabilities to closure within 14 days.
- Cut phishing click rates from 14% to 5% through monthly simulations and short training for 1,200 employees.
- Contained 40 infected endpoints using CrowdStrike, isolating each one within 20 minutes of the first detection.
- Tuned SIEM correlation rules to reduce false positives by 28%, giving analysts more time for real threats.
- Mapped detections to the MITRE ATT&CK framework, closing coverage gaps in five technique categories.
- Wrote Python scripts to enrich indicators of compromise, saving analysts about eight hours a week.
- Supported an ISO 27001 surveillance audit by gathering evidence for 30 controls with no major findings.
- Reviewed firewall rules for [X systems] and removed [X risky or unused rules] to shrink the attack surface.
- Presented monthly risk reports to executives, translating technical findings into business impact for [X teams].
- Led tabletop exercises for [X departments] to test the incident response plan and update contact lists.
- Investigated reported phishing emails and blocked [X malicious domains] across the company mail gateway.
- Enforced multi-factor authentication for [X% of accounts] and helped teams fix their sign-in problems.
Resume summary examples for a Cybersecurity Analyst
Cybersecurity analyst with 5 years of experience in SOC operations and vulnerability management. Skilled in Splunk, CrowdStrike and Nessus, with CompTIA CySA+ and GCIH certifications, plus experience supporting ISO 27001 audits. Turns alerts into clear actions, writes tidy incident reports, and explains risk without jargon to engineers and leadership.
Mid level security professional focused on detection and response in regulated finance. Experienced in incident playbooks, threat hunting and audit support, and comfortable leading a small shift while keeping detailed documentation of every investigation. Strong grounding in NIST and ISO 27001 controls, with audit experience and a calm approach under pressure.
Security graduate with CompTIA Security+ and a home lab in which I practise log analysis, packet capture and vulnerability scanning. Looking for a SOC analyst role where I can learn from senior responders and contribute to monitoring and triage from the start, with a steady habit of writing up what I find.
More resume examples
- Data Analyst resume
- Data Scientist resume
- DevOps Engineer resume
- Frontend Developer resume
- IT Support Engineer resume
- QA Tester resume
- Accountant resume
- Architect resume
- All resume examples by profession